Cloud Encryption 101: Protecting Data at Rest, in Transit, and in Use
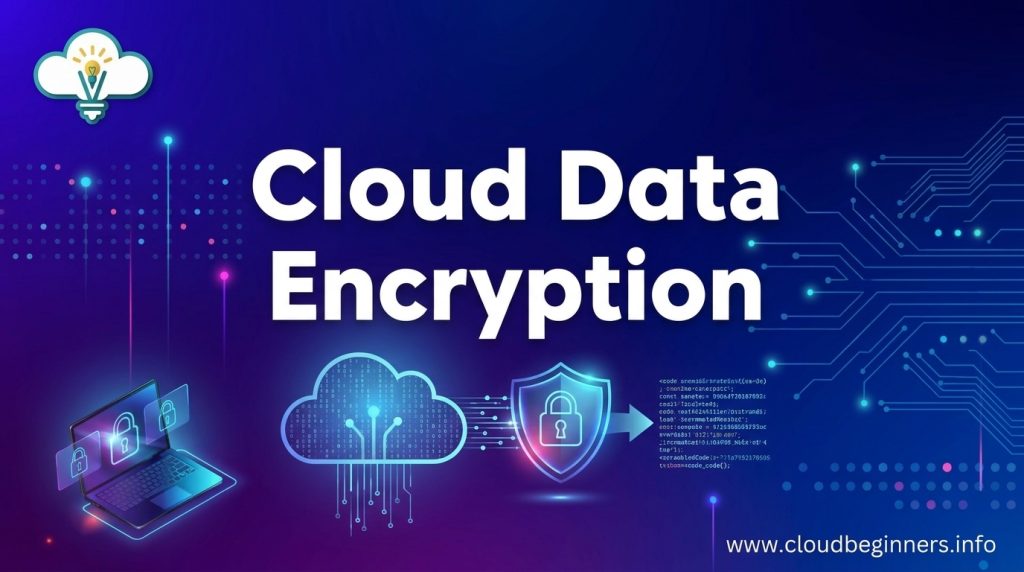
Ever thought about how many times your data passes through unsecured networks each day? If you’re running business operations in the cloud, the answer might keep you up at night.
Let’s cut through the jargon and get real about cloud encryption. This guide will show you exactly how to protect your sensitive information whether it’s sitting in storage, moving between systems, or being processed.
Cloud encryption isn’t just for the paranoid anymore it’s essential for any business using cloud services. With regulations tightening and data breaches making headlines weekly, understanding how to lock down your data at every stage is non-negotiable.
So what’s the difference between protecting data at rest versus in transit? And why is securing data in use the final frontier most companies miss completely?
Understanding Cloud Data Security Fundamentals
A. Why cloud data security matters in today’s digital landscape
Moving your data to the cloud isn’t just convenient; it’s practically essential for modern business. But once your sensitive information leaves your physical control, you’re facing a whole new world of security challenges.
Think about it: your customer data, intellectual property, and financial records are now stored on systems you don’t directly manage. A single breach could cost you millions in damages, regulatory fines, and lost customer trust. The average cost of a data breach?
A staggering $4.35 million in 2022.
Your competitors are just one security slip-up away from accessing your trade secrets. Your customers are one hack away from having their personal information exposed.
B. Key security threats facing cloud-stored data
You’re up against numerous threats when storing data in the cloud:
- Unauthorized access: Anyone with stolen credentials can potentially access your data
- Data breaches: Sophisticated attacks that extract sensitive information
- Malicious insiders: Your own people with legitimate access going rogue
- Inadequate configuration: One misconfigured setting can expose everything
- API vulnerabilities: Weak interfaces between applications create entry points
The most alarming part? These attacks are increasingly sophisticated. Ransomware operators now employ double-extortion tactics; they’ll encrypt your data AND threaten to leak it publicly.
C. The three states of data requiring protection
Your data exists in three distinct states, each requiring specific protection approaches:
- Data at rest: Information stored in databases, file systems, or backups
- Data in transit: Information moving between systems, applications, or users
- Data in use: Information actively being processed in memory or CPU
Each state presents unique security challenges. For example, your data in transit requires different encryption protocols than your stored data. Miss protecting one state, and you’ve left a wide-open vulnerability.
D. Regulatory requirements for cloud data protection
Depending on your industry and location, you’re likely subject to multiple regulations governing how you protect cloud data:
| Regulation | Region/Industry | Key Requirements |
|---|---|---|
| GDPR | Europe | Data minimization, breach notification, right to erasure |
| HIPAA | US Healthcare | Encryption, access controls, audit trails |
| PCI DSS | Payment Card Industry | Encryption, vulnerability management, access restriction |
| CCPA/CPRA | California | Disclosure requirements, opt-out rights, reasonable security |
Non-compliance isn’t an option. GDPR violations can cost you up to 4% of global annual revenue or €20 million, whichever is higher. The regulatory landscape keeps evolving too, with new requirements emerging regularly.
Data at Rest: Securing Stored Information
A. Encryption methods for cloud storage
When storing your data in the cloud, encryption is your first line of defense. The most common methods include:
- AES (Advanced Encryption Standard): Your go-to encryption algorithm, typically using 256-bit keys for maximum security
- RSA: Perfect for securing your encryption keys, using asymmetric encryption with public and private key pairs
- Tokenization: Replaces your sensitive data with non-sensitive placeholders
Client-side encryption gives you complete control—your data gets encrypted before it ever leaves your device. With server-side encryption, your cloud provider handles the encryption process after receiving your data.
B. Key management strategies for data at rest
Your encryption is only as strong as your key management strategy. Consider these approaches:
- Hardware Security Modules (HSMs): Physical devices that safeguard your encryption keys
- Key rotation: Change your encryption keys regularly (every 90 days is a good rule of thumb)
- Split knowledge/dual control: Divide key management responsibilities so no single person has complete access
- Cloud Key Management Services (KMS): Let your cloud provider handle key storage while you maintain control over who can use them
C. Cloud storage security best practices
Boost your cloud security with these practical steps:
- Enable multi-factor authentication for all access to your stored data
- Apply the principle of least privilege; give users only the access they absolutely need
- Classify your data based on sensitivity and apply appropriate encryption levels
- Keep your encryption software updated to patch security vulnerabilities
- Regularly audit who’s accessing your stored data and when
D. Automated security controls for dormant data
Your inactive data needs protection too. Set up these automated controls:
- Data Loss Prevention (DLP): Tools that automatically detect and protect sensitive information
- Auto-encryption policies: Ensure new data gets encrypted immediately upon storage
- Automatic key rotation: Schedule regular key changes without manual intervention
- Retention policies: Automatically delete data that’s no longer needed
- Access monitoring: Get alerts when dormant data is suddenly accessed
E. Case studies of data-at-rest breaches and lessons learned
The 2019 Capital One breach exposed over 100 million customers’ data because of a misconfigured web application firewall. Your takeaway? Regularly audit your security configurations and test them against real-world attack scenarios.
In 2018, Marriott discovered unauthorized access to their Starwood database that had been happening since 2014. The attackers accessed unencrypted passport numbers and payment information. Your lesson: Encrypt ALL sensitive data, not just what regulations require.
The 2021 Microsoft Exchange Server breach affected thousands of organizations using on-premises servers. Your key insight: Keep encryption systems updated with the latest security patches.
Data in Transit: Protecting Information on the Move
A. Transport Layer Security (TLS) protocols explained
When you send data across the internet, it’s like sending a postcard that anyone can read, unless you protect it. This is where TLS comes in. TLS creates a secure tunnel for your data to travel through, keeping prying eyes away.
TLS works through a handshake process:
- Your device and the server say hello
- They verify each other’s identity
- They agree on encryption keys
- Secure communication begins
The latest version, TLS 1.3, offers faster connections and stronger security than older versions. If you’re still using TLS 1.0 or 1.1, you’re basically leaving your front door unlocked.
B. End-to-end encryption implementation
Think of end-to-end encryption as a locked box that only you and your recipient have keys to. Even the delivery person (your service provider) can’t peek inside.
To implement E2EE in your cloud systems:
- Use protocols like Signal for messaging
- Implement PGP for emails
- Ensure encryption keys never leave user devices
- Verify no backdoors exist in your encryption tools
WhatsApp, Signal, and ProtonMail all use E2EE; and you should too if your data is sensitive.
C. Virtual Private Networks (VPNs) and secure tunneling
VPNs create an encrypted tunnel through the public internet. Imagine driving your data through a private underground passage instead of on the open highway.
When setting up VPNs for cloud connections:
- Choose protocols like WireGuard or OpenVPN
- Implement strong authentication
- Ensure no DNS leaks occur
- Use split tunneling selectively
Your cloud provider likely offers their own VPN solution (like AWS Client VPN), but third-party options can work well too.
D. API security for data transfers
APIs are the connective tissue of modern cloud systems, but they’re also potential security weak spots.
To lock down your API data transfers:
- Use OAuth 2.0 and API keys for authentication
- Implement rate limiting to prevent abuse
- Validate all inputs to prevent injection attacks
- Encrypt payloads beyond the transport layer
Don’t fall into the trap of thinking TLS alone protects your API. You need defense-in-depth authentication, authorization, and careful monitoring too.
Remember to rotate your API keys regularly. A static key is like a house key you never change; eventually, someone else will get a copy.
Data in Use: Securing Active Information
A. Confidential Computing Technologies
When you’re processing data in the cloud, it’s at its most vulnerable. Confidential computing addresses this by protecting data while it’s being processed. Think of it as a secure bubble around your computations.
You’ll find this technology especially useful when handling sensitive information like financial data or personal identifiers. Unlike traditional methods that only protect stored or moving data, confidential computing secures your information during active use.
B. Homomorphic Encryption Possibilities
Homomorphic encryption is like a magic trick for your data. It lets you perform calculations on encrypted information without ever decrypting it.
You can analyze sensitive customer data without exposing the underlying information. Though still maturing, this technology offers incredible potential for maintaining privacy while extracting value from your data.
When you implement partially homomorphic encryption, you’ll enable specific operations like addition or multiplication on encrypted data, while fully homomorphic encryption allows any computation.
C. Secure Enclaves and Trusted Execution Environments
Secure enclaves give you isolated processing environments where sensitive code and data stay protected from the rest of the system.
You’ll see technologies like Intel SGX, AMD SEV, and ARM TrustZone creating hardware-level separation between your sensitive operations and potential threats. Your applications can verify they’re running in a legitimate enclave through remote attestation, ensuring your code hasn’t been tampered with.
D. Memory Encryption Techniques
Memory attacks can expose your sensitive data during processing. That’s why memory encryption is crucial.
You’ll want to implement technologies like Intel’s Total Memory Encryption (TME) or AMD’s Secure Memory Encryption (SME) to protect your data while it resides in RAM. These solutions encrypt memory contents automatically, keeping your information safe even if an attacker gains physical access to your hardware.
E. Runtime Application Protection
Your applications need protection during execution. Runtime application protection creates a shield around your running applications.
You’ll benefit from tools that monitor execution flow, detect anomalies, and prevent exploitation in real-time. Consider implementing Runtime Application Self-Protection (RASP) solutions that integrate directly with your application and provide context-aware security.
These tools help you identify and block attacks like code injection, memory corruption, and unauthorized data access while your application is processing information.
Cloud Encryption Implementation Strategies
A. Choosing between provider-managed and client-managed encryption
When setting up your cloud security, you’ll face a critical decision: who controls your encryption keys? Provider-managed encryption is the easy button – your cloud provider handles everything. You don’t need to worry about key management, and implementation is nearly instant.
But there’s a tradeoff. With client-managed encryption, you maintain complete control over your keys. This means nobody (not even your provider) can access your data without your permission. The downside? You’re responsible for safeguarding those keys – lose them, and your data becomes permanently inaccessible.
| Provider-Managed | Client-Managed |
|---|---|
| Easy setup | More complex implementation |
| Lower administrative burden | Complete control |
| Provider could access data | Only you can access data |
| Less technical expertise needed | Requires security expertise |
B. Hybrid encryption approaches for maximum security
Why choose when you can have both? Hybrid approaches give you the best of both worlds. You might use provider encryption for less sensitive data while implementing client-side encryption for your crown jewels.
A smart strategy is encrypting your data twice – once before it leaves your environment (client-side) and then letting the provider add another layer. This creates defense-in-depth that significantly raises the security bar.
C. Balancing security with performance and usability
The security-usability paradox is real. The more encryption you add, the more potential friction you create. Heavy encryption can slow down applications and complicate user experiences.
To find the right balance:
- Implement risk-based encryption (stronger protection for sensitive data)
- Use caching strategies for frequently accessed encrypted content
- Consider hardware acceleration for encryption/decryption operations
- Test performance impacts before full deployment
D. Encryption key rotation and lifecycle management
Your encryption is only as good as your key management. Regular key rotation limits the damage if a key is compromised. Most security standards recommend rotating encryption keys every 6-12 months.
Create a formal key lifecycle policy covering:
- Key generation (using proper entropy sources)
- Distribution (secure channels only)
- Storage (hardware security modules where possible)
- Rotation schedules (automated is best)
- Revocation procedures
- Backup strategies (because losing keys means losing data)
Remember to document your key custody chain carefully. When someone leaves your organization, ensure they can’t take access to encryption keys with them.
Advanced Cloud Encryption Technologies
A. Quantum-resistant encryption preparation
Your cloud security strategy needs to look beyond today’s threats. With quantum computing on the horizon, current encryption methods face real risks. Standard RSA and ECC algorithms that protect your cloud data now could be cracked by quantum computers in hours instead of millennia.
Start preparing by implementing quantum-resistant algorithms alongside your existing encryption. The NIST has already selected several post-quantum cryptography (PQC) candidates you can integrate into your security framework. These include lattice-based cryptography and hash-based signature schemes that stand up to quantum attacks.
Don’t wait for quantum computers to arrive before acting. Implement crypto-agility in your cloud architecture now so you can swap encryption methods without rebuilding your entire infrastructure.
B. Blockchain for enhanced cloud security
Blockchain isn’t just for cryptocurrency. You can leverage this technology to strengthen your cloud security posture through immutable audit trails and decentralized authentication.
When you implement blockchain in your cloud security:
- Your data access logs become tamper-proof
- Security events get time-stamped and verified across distributed nodes
- Access controls gain an extra verification layer
Many cloud providers now offer blockchain-as-a-service options that integrate with your existing security frameworks. This approach particularly shines when you need to prove compliance or demonstrate data integrity to regulators or customers.
C. Zero-knowledge proofs for privacy protection
Zero-knowledge proofs solve one of your biggest cloud privacy challenges: proving something without revealing sensitive data. This cryptographic method lets you verify transactions or identity without exposing the underlying information.
When handling sensitive customer data in the cloud, you can use ZKPs to:
- Authenticate users without storing actual credentials
- Verify financial transactions without revealing account details
- Confirm compliance without exposing protected data
The beauty of zero-knowledge proofs is in maintaining privacy while still enabling necessary verification processes. Major cloud platforms now offer ZKP-based services for identity management and transaction verification.
D. Multi-party computation in cloud environments
Multi-party computation (MPC) transforms how you handle sensitive operations in the cloud. With MPC, you can process encrypted data without ever decrypting it at any single point.
Think about analyzing healthcare data across multiple organizations without revealing patient details, or running financial models on sensitive data while keeping it protected. MPC makes this possible through cryptographic protocols that split computation across multiple servers.
To implement MPC in your cloud environment:
- Identify sensitive workflows that require shared computation
- Deploy MPC-enabled services through your cloud provider
- Configure data inputs to remain encrypted throughout processing
This approach drastically reduces your attack surface because there’s never a point where all the sensitive data is exposed in one place.
Practical Steps for Enhanced Cloud Security
Creating a comprehensive cloud encryption strategy
Building a rock-solid encryption strategy isn’t just smart; it’s essential. Start by mapping all your data flows and classifying information based on sensitivity. This gives you clarity on what needs the strongest protection.
Your strategy should include:
- Clear policies for encryption key management
- Standards for encryption algorithms (AES-256 is your friend)
- Rules for data handling across its entire lifecycle
Don’t treat this as a one-time task. Your encryption strategy needs regular reviews as your cloud footprint grows and evolves.
Security assessment and penetration testing
You can’t protect what you don’t understand. Regular security assessments help you spot weaknesses before hackers do. Schedule quarterly vulnerability scans and annual penetration tests targeting your encryption implementation.
Ask tough questions:
- Are your encryption keys properly secured?
- Could someone bypass your encryption during data transfers?
- How strong is your key rotation process?
White-hat hackers can be your best allies. Hire external security experts to test your defenses without mercy.
Employee training for data protection
Your security is only as strong as your least-trained team member. Create engaging training programs that help your staff understand:
- Why encryption matters (with real-world examples)
- How to handle sensitive data correctly
- Warning signs of potential security breaches
Make this training interactive and relevant to each role. The marketing team needs different guidance than your developers. Reward security-conscious behavior and create a culture where asking questions about data protection is encouraged.
Incident response planning for encryption failures
Even perfect systems fail. You need a battle plan for encryption emergencies that includes:
- Clear steps to contain the breach
- A communication strategy for stakeholders
- Procedures to identify what data was exposed
Run simulations regularly. Your team should know exactly what to do if encryption keys are compromised or if encrypted data is somehow exposed.
Continuous monitoring and security updates
Encryption isn’t “set it and forget it” technology. Set up automated monitoring systems that alert you to unusual access patterns or potential encryption failures. Stay current with security bulletins and patch vulnerable systems immediately.
Create dashboards that give you real-time visibility into your encryption status. Schedule monthly reviews of your encryption tools and processes to identify areas for improvement.
Remember that cloud providers regularly update their encryption offerings. Take advantage of these improvements—what was secure last year might not meet today’s standards.
The ever-evolving landscape of cloud security demands a comprehensive approach to encryption. By implementing robust strategies for protecting data at rest, in transit, and in use, organizations can significantly reduce their vulnerability to breaches and unauthorized access.
From storage encryption and secure transport protocols to homomorphic encryption and secure enclaves, the technologies available today offer unprecedented levels of protection for your sensitive information.
As you enhance your cloud security posture, remember that encryption is just one component of a broader security framework.
Combine strong encryption practices with proper key management, regular security assessments, and employee training to create a truly resilient cloud environment. By taking these practical steps today, you’ll be better positioned to face the security challenges of tomorrow’s increasingly complex digital landscape.
I’ve built a platform that shows you how you can build the right cybersecurity skills to help businesses achieve their cloud security goals while you’re also building the career you love. Check it out here and start working on projects that get you hired.
The Author