The 5 Most Overlooked Cloud Security Settings (And How to Enable Them)
The 5 Most Overlooked Cloud Security Settings (And How to Enable Them)
You’ve spent thousands on cloud infrastructure, implemented robust security policies, and still wake up in a cold sweat wondering: “What am I missing?”
Here’s the painful truth: most cloud security breaches aren’t from sophisticated attacks. They’re from overlooked configuration settings hiding in plain sight.
Your cloud security is probably more vulnerable than you think. Those default settings you never bothered to change? They’re the digital equivalent of leaving your keys in the ignition with the engine running.
This guide will show you the five most commonly overlooked cloud security settings that leave your organization exposed to unnecessary risk.
What’s the setting that 78% of security professionals admit they’ve never even checked? It might be the very thing keeping your door wide open to attackers.
Understanding Cloud Access Controls
Why default settings aren’t enough
Default cloud configurations are like buying a new car and driving away without adjusting your seat or mirrors. Sure, it’ll move, but it’s not safe for you specifically. When you set up your cloud environment, providers give you a basic security template that works for everyone… which means it works perfectly for no one.
Most default cloud settings prioritize ease of use over security. Think about it: cloud providers want you to start using their platform quickly, not get stuck in configuration hell.
Your AWS S3 buckets might start with public access, your Azure blob storage could allow anonymous access, and your Google Cloud IAM policies might be more permissive than you realize.
The risks of overlooked permissions
You know that feeling when you realize you’ve left your front door unlocked all day? That’s nothing compared to overlooked cloud permissions.
When you don’t tighten access controls beyond the defaults, you’re practically rolling out a red carpet for both insider threats and external attackers. Excessive permissions create a larger attack surface; each unnecessary access point is another potential entry for bad actors.
The scary part? Many organizations don’t discover these issues until after a breach. By then, attackers might have:
- Stolen sensitive customer data
- Deployed crypto-mining software on your dime
- Established backdoors for future access
How attackers exploit weak access controls
Cybercriminals love weak cloud access controls like kids love candy stores. Here’s how they typically exploit them:
First, they scan for common misconfigurations using automated tools. Once they spot a weakness maybe an over-permissive IAM role or a misconfigured security group—they’ll move laterally through your environment.
Your weak spot might be something simple: service accounts with admin privileges, over-generous API keys, or cross-account access policies you forgot about months ago. Attackers can leverage these to escalate privileges until they reach your crown jewels.
Remember: in cloud security, you’re only as strong as your weakest access control.
Multi-Factor Authentication (MFA) Settings
Why MFA is frequently disabled
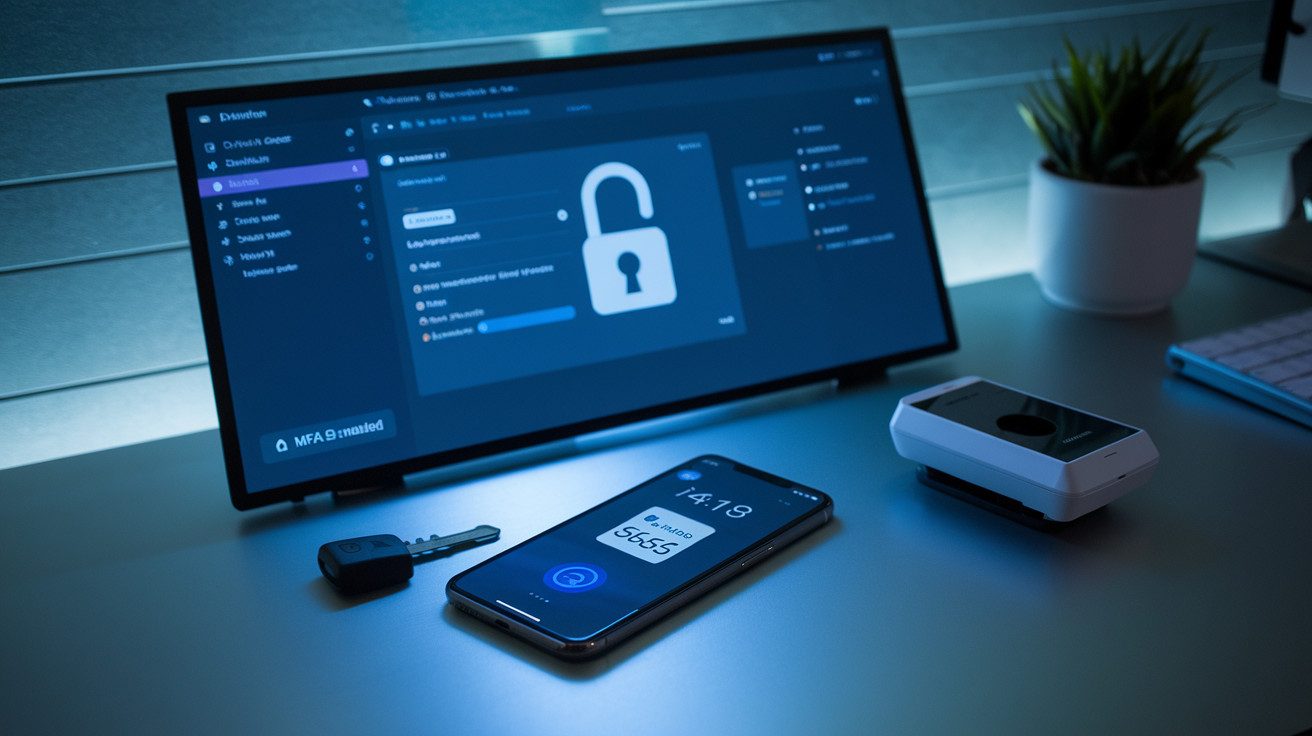
Truth bomb: you’re probably letting convenience win over security. Most organizations disable MFA because it adds “friction” to the login process. Your team complains about the extra step, executives push back on anything slowing them down, and suddenly that critical security feature gets shelved.
Technical complexity is another culprit. Maybe you tried implementing MFA but ran into compatibility issues with legacy systems or struggled with the configuration. Or perhaps you’re worried about lockout scenarios – what happens when employees lose their authentication devices?
Cost considerations also play a role. Some advanced MFA options require additional licensing or hardware purchases that weren’t in your budget.
Setting up MFA for admin accounts
Start here – no excuses. Admin accounts are your crown jewels and need maximum protection:
- Log into your cloud console and navigate to Identity/User settings
- Enable MFA for all admin accounts
- Choose your authentication methods (app-based is generally best)
- Set a short enforcement period (24-48 hours)
- Communicate clearly with admins about the change
Implementing MFA across your organization
Ready to roll this out company-wide? Smart move.
First, segment your users based on access levels and data sensitivity. Create a phased approach starting with high-privilege accounts.
Next, select user-friendly authentication options – smartphone apps usually work best, but consider SMS or hardware tokens for specific use cases.
Monitoring MFA compliance
You can’t improve what you don’t measure. Set up regular compliance reporting to track:
- MFA enrollment rates by department
- Authentication failures and patterns
- Exception requests and approvals
Configure alerts for suspicious activities like multiple failed MFA attempts or disabled authentication.
Data Encryption Configuration
A. Identifying unencrypted cloud storage
You’ve probably got tons of data sitting in cloud storage right now, but do you know which buckets aren’t encrypted? Start by running a cloud security assessment using your provider’s tools (AWS Config, Azure Security Center, or Google Security Command Center).
Look for the telltale red flags: storage marked as “unencrypted” or “encryption disabled.” Many cloud dashboards now feature security score cards that highlight these vulnerabilities front and center.
B. Enabling at-rest encryption
Turning on encryption for your stored data is surprisingly simple. In most cloud platforms, it’s just a checkbox during bucket creation or a toggle in your existing storage settings.
Head to your storage configuration panel and enable “default encryption” or “encrypt at rest.” If you’re using AWS S3, you’ll see options for SSE-S3, SSE-KMS, or SSE-C encryption types. Don’t overthink it; even the basic provider-managed encryption is dramatically better than nothing.
C. Configuring in-transit encryption
Your data needs protection when it’s moving too. Make sure you’re enforcing HTTPS for all API connections to your storage. Update your bucket policies to reject non-SSL requests with simple statements that require secure transport.
In AWS, add condition keys like aws:SecureTransport set to “true” in your IAM policies. For Azure, just toggle “Secure transfer required” to On in your storage account settings.
D. Managing encryption keys securely
Who holds your encryption keys makes all the difference. For sensitive data, skip the provider-managed keys and set up your own key management service (AWS KMS, Azure Key Vault, or Google Cloud KMS).
Establish key rotation schedules; quarterly is a good starting point. Create separate keys for different environments and projects. Remember to back up your master keys in a secure, offline location; lose these and your data becomes permanently unreadable.
E. Testing encryption effectiveness
Don’t just assume your encryption is working; prove it. Try accessing your encrypted data through unauthorized channels or without proper key permissions. Use your cloud provider’s logging features to verify encryption is happening as expected.
Set up alerts for any attempted access to encryption keys or changes to encryption settings. Run periodic encryption audits using tools like AWS Trusted Advisor or Azure Advisor to catch any storage that might have slipped through your configuration process.
Network Security Boundaries
Finding overlooked firewall rules
You’ve probably set up the basic firewall rules for your cloud environment, but those easy-to-miss settings are what hackers love to exploit. Check your inbound rules – do you have any “temporary” open ports that somehow became permanent? It happens more than you’d think.
Run a quick audit of your cloud firewall settings. Look for:
- Rules with “Any” source IP addresses
- Overly permissive port ranges
- Outdated rules for decommissioned services
- Rules created for “testing” that never got removed
Most cloud breaches don’t come from sophisticated attacks but from these simple misconfigurations that slip through the cracks during your busy day.
Configuring proper IP restrictions
Those default “allow all” settings might make deployment easier, but they’re a security nightmare waiting to happen. Tighten up your IP restrictions by implementing allowlists instead of blocklists.
Only permit traffic from IPs that actually need access:
- Your company’s office IP ranges
- Approved remote worker VPN addresses
- Partner systems with legitimate integration needs
Remove those broad 0.0.0.0/0 rules that basically invite anyone on the internet to try their luck with your systems. Yes, it requires more management, but the protection is worth every minute spent.
Implementing network segmentation
Think your cloud environment is one big neighborhood? Break it up! Network segmentation is your best friend for containing potential breaches.
Start by grouping similar resources:
- Separate production from development environments
- Isolate database layers from application layers
- Create boundaries between different customer data stores
When you segment properly, even if attackers breach one area, they can’t easily move laterally through your entire cloud infrastructure. It’s like having security checkpoints between different zones of your cloud.
Audit Logging and Monitoring
Enabling comprehensive audit trails
Think you’ve got your cloud security locked down? Not if you’re ignoring audit logs. Most cloud providers hide these settings deep in their consoles, but they’re absolute gold for tracking who did what in your environment.
To set this up properly:
- Go to your security settings and crank up logging to “verbose” mode
- Make sure you’re capturing both successful and failed actions
- Track user identity, IP address, timestamp, and resource details
- Don’t forget API calls – those sneaky automated processes need watching too
AWS CloudTrail, Azure Monitor, and Google Cloud’s Operations Suite all offer robust audit capabilities that you’re probably not using to their full potential. Enable them now – not after something goes wrong.
Setting up automated security alerts
What good are logs if nobody’s watching them? Alerts are your early warning system, but they’re useless if they’re flooding your inbox with noise.
Here’s how to set up alerts that actually matter:
- Configure alerts for privilege escalations and permission changes
- Set thresholds for unusual data transfers (both in and out)
- Create alerts for geographic anomalies (logins from unexpected locations)
- Establish baselines for normal activity first, then alert on deviations
Configuring log retention policies
Your logs are worthless if they vanish before you need them. Most organizations set default retention too short, leaving them blind during investigations.
Smart retention looks like this:
- Store security logs for at least 1 year (longer for regulated industries)
- Implement tiered storage to balance cost (hot storage for recent logs, cold for archives)
- Don’t compress logs you’ll need to search regularly
- Encrypt archived logs to maintain their chain of custody
Creating custom security dashboards
Pre-built dashboards rarely show what you actually need. Creating custom views gives you instant visibility into your specific security concerns.
Build these dashboards today:
- Identity and access management changes dashboard
- Failed authentication attempts with geographic mapping
- Resource configuration changes tracker
- Data exfiltration monitoring panel with threshold indicators
Your custom dashboards turn overwhelming log data into actionable intelligence. They’re your daily security newspaper – make sure they tell the right story.
Protecting your organization in today’s cloud-first world requires attention to often neglected security settings.
By properly configuring access controls, implementing MFA across all user accounts, enabling encryption for data both in transit and at rest, establishing robust network boundaries, and setting up comprehensive logging and monitoring, you can significantly reduce your attack surface and better protect your sensitive information.
Don’t wait for a security incident to highlight these vulnerabilities in your cloud environment. Take proactive steps today to review and enable these five critical security settings.
Be aware that cloud security is a shared responsibility; while providers secure the infrastructure, you must properly configure and maintain the security of your applications and data. Start with an audit of your current settings and systematically address any gaps you discover.
I’ve also built a platform that shows you how to build the right hands-on cybersecurity skills to help businesses achieve their cloud security goals while you build the career you love for a better, higher-paying reward. Check it out here and start working on projects that will help you get hired.
The Author